How to combat money laundering, with real enforcement cases to learn from
Every institution in this article had an AML program. Wachovia had one. HSBC had one, then rebuilt it under a five-year monitorship, then failed again. TD Bank had one that its own internal auditors flagged as inadequate for years.
The gap between having a program and having one that works is where enforcement happens. Below are six strategies for closing it, and six cases showing what it costs when they are not closed.
6 ways to combat money laundering
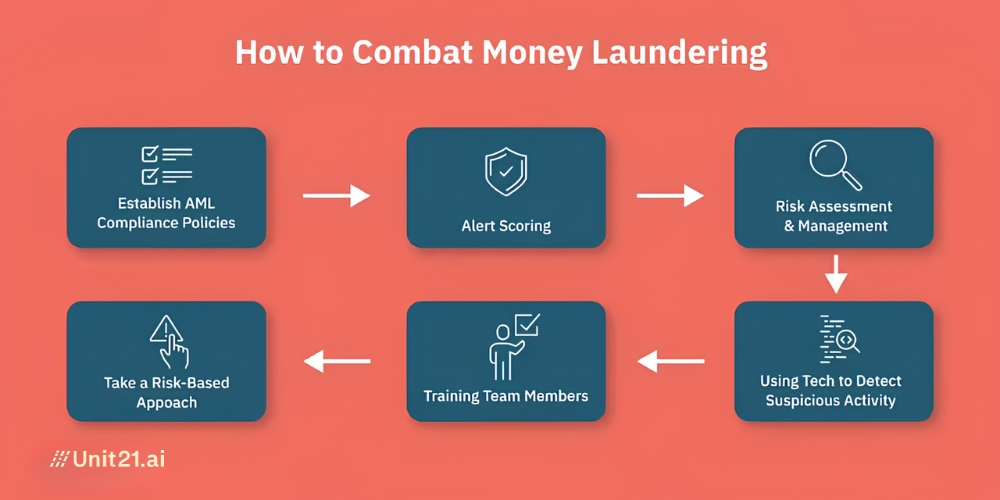
1. Establish AML compliance policies
Compliance policies define the framework: what the organization does, who is responsible, and what happens when something is escalated. The policy has to be written down and accessible to everyone, not held by the compliance team alone.
The part institutions get wrong is treating the policy as the deliverable. A policy nobody outside compliance has read has no operational effect, which is exactly what several of the cases below demonstrate.
2. Prioritize KYC processes
Verifying identity through KYC procedures is required under AML regulations, and it is the first control in the customer lifecycle.
The requirement is not just to verify who someone is, but to establish what they are expected to do. Without an expected-activity baseline captured at onboarding, ongoing monitoring has nothing to compare against, which is how customers whose behavior changes go undetected for years.
3. Detect suspicious patterns
The most productive control is monitoring transaction patterns across the whole relationship rather than at a single point.
Patterns worth watching: transfers to offshore accounts, many small-value transactions to the same recipient, regular transfers to high-risk or sanctioned jurisdictions, and activity inconsistent with a customer's stated purpose. Coverage matters more than sophistication here. TD Bank's failure was not that its rules were wrong, it was that 92% of transaction volume was not monitored at all.
4. Use technology that your team can change
Manual screening does not scale, and regtech software handles transaction monitoring, suspicious activity reporting, and regulatory recordkeeping at volume.
The capability that actually matters is whether your team can change detection logic without waiting on someone else. TD Bank added no new monitoring scenarios between 2014 and 2022. A program that cannot adapt at the speed typologies change will eventually be examining a risk picture that no longer exists.
5. Train team members
Training compliance staff is necessary. Training everyone else is what makes it work.
The recurring theme in enforcement is that someone knew. Internal auditors at TD Bank flagged the gaps. A Danske Bank whistleblower raised the Estonian branch. Regulators warned Standard Chartered in 2004 and Capital One repeatedly. Awareness was not the failure. Escalation that reached someone with authority to act was.
6. Take a risk-based approach
A risk-based approach means understanding the specific risks your organization faces and building controls proportionate to them, rather than applying one standard everywhere.
Regulators have moved decisively in this direction, away from prescriptive rules. In practice it means customer risk ratings drive the depth of due diligence and the sensitivity of monitoring, and it means being able to show an examiner the assessment your controls trace back to.
6 real enforcement cases to learn from
Negligence does not exempt an institution. Banks, exchanges, and other financial institutions that fail to prevent and report money laundering are penalized regardless of intent.
1. TD Bank, $3.09 billion, 2024
The largest penalty ever imposed under the Bank Secrecy Act, and the first time a US bank pleaded guilty to conspiracy to commit money laundering.
The finding was about program design rather than intent. Between 2014 and 2022, TD added no new transaction monitoring scenarios and made no material changes to existing ones. Over roughly six years, 92% of transaction volume, about $18.3 trillion, went unmonitored. Internal auditors and federal regulators both flagged the gaps. The bank was operating under a cost paradigm that deferred AML investment.
The lesson: a static program decays into an inadequate one. Coverage has to be measured and reported, and monitoring scenarios have to keep pace with the business they cover.
2. Danske Bank, $2.059 billion, 2022
Danske acquired Sampo Bank in 2007. Russia's central bank raised concerns about suspicious activity at the Estonian branch, alerting Danish and Estonian authorities. No immediate action followed.
By February 2014, through a combination of internal audits, information from regulators, and an internal whistleblower, Danske knew its Estonian non-resident customers were engaged in highly suspicious and potentially criminal transactions, and that the branch's AML program did not meet the bank's own standards. Rather than disclose this, the bank lied to its US correspondent banks about the state of the branch's AML controls and transaction monitoring in order to keep its dollar accounts open. Roughly $160 billion moved through US banks from the branch between 2008 and 2016.
On 13 December 2022, Danske pleaded guilty to one count of conspiracy to commit bank fraud and agreed to forfeit $2.059 billion. The SEC separately settled charges of misleading investors about the Estonian program for $413 million.
The lesson: this was not only inadequate policy, it was active concealment. The charge was fraud on correspondent banks rather than laundering, which is worth noting: misrepresenting your own AML program to a partner institution is itself the crime. Acquisitions need AML diligence applied to every entity they bring in.
3. HSBC, $1.9 billion, 2012
In the 1990s, HSBC did business with countries on international sanctions lists including Iran, Cuba, Burma, Libya, and Sudan, concealing the origin of funds to circumvent AML controls. Group leadership learned of the practice in 2000 and allowed it to continue until 2006, while also scaling back the AML program.
Mexican and Colombian cartels exploited the resulting gaps between 2006 and 2010, moving $881 million through the bank. The $1.9 billion penalty came with five years of independent monitoring. In 2017 HSBC again admitted inadequate controls, and in 2021 the UK fined it a further £64 million.
The lesson: remediation under a monitorship is not the same as a working program. HSBC failed again after being rebuilt once.
4. Standard Chartered, penalized three times: $667 million, $300 million, $1.1 billion
The clearest case on this list of remediation that did not take.
2012: $667 million for processing transactions in violation of sanctions on Iran, Myanmar, Libya, and Sudan between 2001 and 2007. The bank entered a deferred prosecution agreement with the DOJ and accepted an independent monitor.
2014: a further $300 million from the New York Department of Financial Services, plus restrictions on its dollar-clearing business, after its compliance systems failed to detect high-risk transactions largely originating in Hong Kong and the UAE. Two years after the first penalty, under a monitor.
2019: $1.1 billion in April, $947 million to five US agencies and £102 million to the UK Financial Conduct Authority. The Treasury found the bank had processed nearly 10,000 transactions between 2009 and 2014 moving $438 million in violation of sanctions, acting with what it called reckless disregard. The FCA found the bank had accepted high-risk customers without adequate due diligence, including one who opened an account with a suitcase containing 3 million dirhams, roughly $625,000 in cash, and no evidence of where it came from.
Since 2012, NYDFS alone has penalized Standard Chartered more than $1.1 billion across four separate actions.
The lesson: repeat findings compound, and a monitorship is not a control. Screening against sanctioned jurisdictions and entities is not something you can partially implement, and regulators price a second and third failure very differently from a first.
5. Westpac, AU$1.3 billion, 2020
Westpac permitted 23 million breaches of Australian AML and counter-terrorism financing rules. That is the count of individual breaches, not the value. It failed to report and keep records for international transfers, some linked to child exploitation in Southeast Asia.
In 2020 Westpac was ordered to pay AU$1.3 billion, the largest civil penalty in Australian corporate history at the time.
The lesson: reporting obligations are counted per transaction. Systematic under-reporting produces penalties that scale with volume, which is why a coverage gap is more dangerous than a tuning problem.
6. Wachovia, $160 million, 2010
Between 2004 and 2007, Wachovia processed $378.4 billion for Mexican currency exchange houses, casas de cambio, linked to the Sinaloa and other cartels. Cash from US drug sales moved to Mexico, was deposited into local accounts under looser controls, then wired back into Wachovia via correspondent accounts.
Martin Woods, a senior AML officer who joined Wachovia in 2005, raised the concerns internally and filed suspicious activity reports. He was largely ignored. Pressure from the US attorney's office in 2007 eventually led the bank to cut ties with some of the exchange houses, and Woods took the case to the DEA himself.
In March 2010, Wachovia entered a deferred prosecution agreement, charged with failing to maintain an effective AML program, and paid $160 million: $110 million in forfeited proceeds and a $50 million fine. Around $13 million had passed through its correspondent accounts to buy aircraft for trafficking; more than 20,000 kilograms of cocaine were later seized from those planes.
The lesson: correspondent and intermediary relationships inherit the AML weaknesses of the institution on the other side. Monitoring source of funds through those channels is a separate control from monitoring your own customers, and it is the one most often absent.
What these cases have in common
Four patterns run through all six.
Someone knew before the regulator did. Internal audit, a whistleblower, or an earlier examination flagged the problem. The failure was escalation, not detection.
The program existed on paper. Every one of these institutions had documented policies. What was missing was operational coverage matching the business.
Coverage gaps beat tuning problems. The largest penalties involve activity that was never examined at all, rather than activity examined badly.
Remediation commitments get tested. HSBC and Standard Chartered were both penalized again after promising to fix things, Standard Chartered twice, while under an independent monitor. Regulators price a second failure differently.
And the price is rising steeply. Wachovia's $160 million in 2010 was, at the time, the largest penalty ever imposed for a Bank Secrecy Act violation. Fourteen years later TD Bank paid $3.09 billion, roughly nineteen times as much, for a failure of the same basic kind. Whatever a coverage gap cost your predecessors, it costs more now.
Moving from lessons learned to following regulations
No financial organization is immune to not doing enough, regardless of headcount or budget. What separates the institutions that pass examination from the ones in this article is usually not effort. It is whether coverage is measured, whether findings reach someone who can act, and whether detection logic can change when the risk does.
For detail by business type and jurisdiction, read our chapter on anti-money laundering regulations organizations should know.
If you are still getting acquainted with how money laundering works, jump back to the three stages of money laundering.
How Unit21 helps close these gaps
Three of the four patterns above are infrastructure problems as much as governance ones.
Coverage you can see. Transaction monitoring rules are explicit and auditable, so what is and is not covered is visible rather than assumed. That is the specific failure that produced the largest penalty on this list.
Detection logic your team controls. Rules are written and tuned in a no-code interface by the people who understand the risk, and tested against historical data before going live. A typology that appears this week can be caught this week, not next quarter.
Findings that reach the work. Case management and regulatory filing run on the same platform as detection, so outcomes feed back into tuning instead of sitting in a report. Unit21's AI Agents handle investigation assembly, gathering evidence, mapping entities, and drafting narratives, with every action logged including which agent configuration was running at the time.
For more on how that works in practice, see our practitioner's guide to agentic AI for AML.
To see it against your own program, book a demo.
Frequently asked questions
What is the most effective way to combat money laundering?
There is no single control. The most consequential factor across enforcement cases is coverage: whether all relevant activity is actually monitored. The largest penalties involve transaction volume that was never examined, rather than transactions examined poorly.
What is the largest AML fine ever issued?
TD Bank's roughly $3.09 billion penalty in October 2024 is the largest ever under the US Bank Secrecy Act. It was also the first time a US bank pleaded guilty to conspiracy to commit money laundering.
Can a financial institution be penalized if no money was actually laundered?
Yes. An inadequate AML program is a violation in its own right. Regulators penalize the gap between what a program claimed to cover and what it actually covered, independent of whether laundering is proven.
Why do banks keep failing AML examinations after being fined?
Because remediation is often treated as a project rather than an operating change. HSBC and Standard Chartered were both penalized a second time after committing to fix their programs. A program that cannot adapt as the business and typologies change will drift back out of adequacy.
What is a risk-based approach to AML?
Building controls proportionate to the specific risks an organization faces, rather than applying uniform standards. Customer risk ratings drive the depth of due diligence and the sensitivity of monitoring, and every control should trace back to a documented risk assessment.
How often should an AML program be reviewed?
At minimum annually, and whenever something material changes: a new product, payment rail, customer segment, jurisdiction, or acquisition. TD Bank's program went eight years without material change, which is the clearest available illustration of why.
Next chapter: Anti-money laundering regulations financial organizations should knowPrevious chapter: The three stages of money laundering
Gal Perelman is the Product Marketing Lead at Unit21, where she spearheads go-to-market strategies for AI-driven risk and compliance solutions. With over a decade of experience in the fintech and fraud sectors, she has led high-impact launches for products like Watchlist Screening and AI Rule Recommendations.
Previously, Gal held marketing leadership roles at Design Pickle, Sightfull, and Lusha. She holds a Master’s degree from American University and a Bachelor’s from UCLA, and is dedicated to helping banks and fintechs navigate complex regulatory landscapes through innovative technology.